
Permission-Aware RAG: How to Stop AI From Showing Users Documents They Shouldn't See
Understand how an enterprise RAG system can carry document permissions into retrieval and test that restricted information stays out of AI answers.
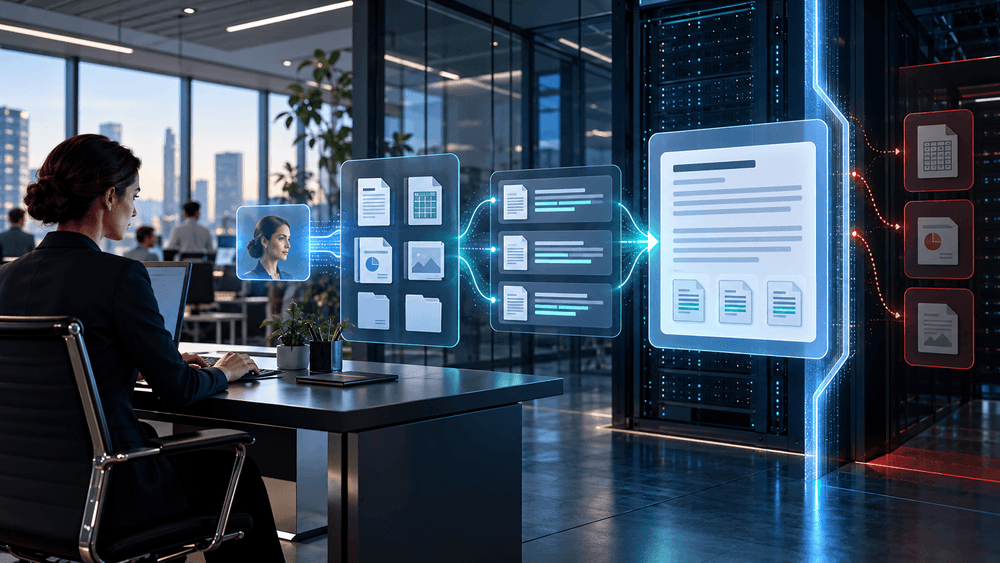
An AI answer can reveal a restricted document even when the employee never opens that document. If the search system retrieves a confidential passage and sends it to the model, the information has already crossed an access boundary. This is why enterprise AI search must apply permissions during retrieval, before the answer is generated.
Permission-aware retrieval-augmented generation, or RAG, connects the employee's identity to the access rules of the original sources. It lets an assistant search useful company information while limiting every answer to material that the employee is authorised to see. The design is more involved than adding a filter after a chat response, but it is central to a trustworthy system.
The Risk Behind a Helpful Answer
Imagine a project manager asks, “What did we agree with this client about the delivery deadline?” The repository contains a contract for that client, a draft for another client and an internal commercial negotiation note. A broad search may retrieve all three because they are topically similar. If the model receives restricted passages, it may mention terms the manager should not see.
The problem is not that the model made up information. It used real company information without the right access check. A source link does not solve this if the answer itself reveals the confidential detail. Permissions need to govern which passages can enter the model's context.
Our enterprise RAG architecture guide explains the full flow from documents to answers. This article focuses on the identity and retrieval boundary within that flow.
Use the Employee's Identity
The application should authenticate the person asking through the organisation's identity system. It then needs the employee's user and group context, or another trusted representation of their permissions. The assistant should not accept a user-supplied claim such as “I am on the finance team” as proof of access.
Some sources use project groups, others use folder permissions or document-level access lists. A company may also restrict customer data by account assignment. The retrieval layer needs to translate these rules into a check it can enforce for each query.
Administrative access to the search index is different from an employee's right to see a source. A connector may have broad technical rights to read files for indexing. That does not mean the assistant can use all of those files for every user.
Carry Source Permissions Into Retrieval
One approach stores permission metadata alongside each indexed document or chunk. At query time, the search request includes the authenticated employee's identity or authorised groups, and the system filters out content that does not match. Another approach checks rights against the source when a result is retrieved. The right design depends on the repository and how quickly rights change.
Azure AI Search's document-level access guidance describes security filters and other approaches to excluding documents a user cannot access. It also makes clear that the application must pass the right identity context. A search index cannot infer a person's permissions from their question.
The filter should apply before passages are passed to the model or shown as search snippets. When content is split into chunks, each chunk must retain the appropriate permissions from its parent document. Losing access metadata during parsing or chunking can create a leak even if the original file is protected.
Handle Changes, Revocation and Deletion
Access is not static. Employees move between projects, a contract becomes confidential or a file is deleted. An index that keeps an old access list may continue returning material after the source has changed.
Define how permission updates reach the search system and how long the delay can be. A sensitive repository may require a live check, frequent synchronisation or a design that fails closed when permission data is unavailable. The organisation also needs a process to remove deleted content from search and from any answer cache.
Group membership can be complex, especially where nested groups or external partners are involved. Test those cases explicitly. A system that works for simple departmental folders may behave differently with project-specific permissions and shared customer spaces.
Cite Sources Without Exposing Them
Source citations help employees verify answers, but the citation itself must respect access rights. A title, file path or preview snippet can disclose sensitive information even when opening the link is blocked. The assistant should only display metadata and excerpts the user is allowed to see.
Logs create another access boundary. Administrators may need traces showing which documents were retrieved to investigate an error, but those traces can contain sensitive passages. Logging, retention and administrator permissions should be part of the security design, not an afterthought.
A user who cannot see a source should receive an honest response such as “I could not find an answer in the information available to you.” The assistant should not hint that a restricted document exists or paraphrase its contents.
Test With Denied Results, Not Only Successful Ones
Build a test set with users from different teams and projects. Ask a question for which an authorised employee should receive a source-linked answer, then ask the same question as someone without access. Repeat after changing a group membership and after deleting or restricting a document.
Also test indirect disclosure. A user may ask for a summary of a client, a comparison of contracts or a list of projects matching a confidential name. The application needs to apply the same access rules to those broad questions as it does to an exact document lookup.
The goal is not simply to prevent a dramatic leak in a demonstration. It is to make everyday retrieval behave consistently with the company's existing access model. Codativity can help design and test this permission boundary alongside hybrid retrieval, so the assistant finds useful evidence only from sources each employee may use.
4/11/2026
Contact Us
701, Opal Tower Business Bay, Dubai United Arab Emirates
P.O.Box 126732
Let's Work Together
© 2016 - 2026 Codativity Software Solutions. All Rights Reserved.